Privacy Policy
How this document works
Karifin serves clients in Lithuania and elsewhere in the EU, and in the United Kingdom. Since Brexit these are two separate legal regimes: the EU GDPR applies in the former, and the UK GDPR — together with the Data Protection Act 2018 and the Data (Use and Access) Act 2025 — applies in the latter. The substance is close, but the regulator, the transfer mechanism, and the governing law differ.
Rather than maintaining two separate contracts that inevitably drift apart, this document uses one framework with a jurisdiction schedule. You elect the applicable regime for each client at the front of the DPA, and the clauses tagged EU or UK take effect accordingly. Where a clause carries no tag, it applies to every engagement.
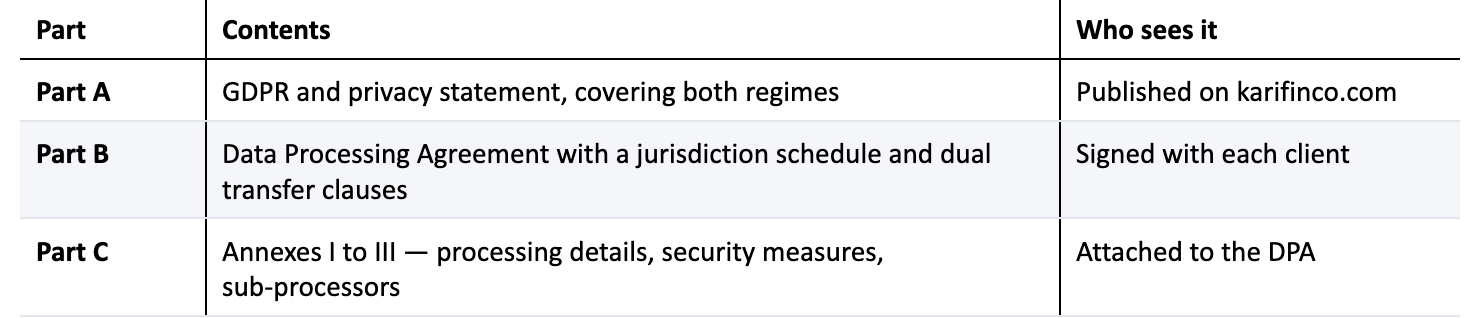
PART A · FOR PUBLICATION ON KARIFINCO.COM
GDPR and privacy statement
Last updated: [19/08/2026]. This statement explains how Karifin & Co handles personal data — both the data we hold about visitors to this website and prospective clients, and the data our clients entrust to us when we deliver accounting, payroll, and CFO services.
1. Who we are
1.1 Karifin & Co ("Karifin", "we", "us") is a finance and accounting consultancy providing bookkeeping, management reporting, payroll, tax compliance, and virtual CFO services to businesses in the European Union, the United Kingdom, the United Arab Emirates, and Bangladesh.
1.2 Registered office: [FULL REGISTERED ADDRESS]. Registration number: [COMPANY REGISTRATION NUMBER].
1.3 For any question about how we handle personal data, contact our data protection contact point at [privacy@karifinco.com] or write to us at the address above. We aim to respond substantively within five working days.
2. Which law applies to you
2.1 If you are in the EEA, or your personal data reaches us through a client established in the EEA, the EU GDPR (Regulation (EU) 2016/679) applies, together with the national implementing law of the relevant member state. For our Lithuanian clients this includes the Republic of Lithuania Law on Legal Protection of Personal Data.
2.2 If you are in the United Kingdom, or your personal data reaches us through a UK-established client, the UK GDPR applies, together with the Data Protection Act 2018 and the Data (Use and Access) Act 2025.
2.3 Where both apply — for example a group with entities in Vilnius and London — we apply whichever standard is higher in respect of each obligation.
3. The two roles we act in
3.1 When you visit this website, subscribe to our newsletter, or contact us about our services, we act as a data controller. We decide what data to collect and why.
3.2 When we deliver services under a client engagement — processing your employees' payroll, recording your supplier invoices, preparing your management accounts — we act as a data processor. Our client is the controller. We process that data only on the client's documented instructions, under the Data Processing Agreement described in section 9.
3.3 Sections 4 to 8 describe our activities as a controller. Section 9 describes our obligations as a processor.
4. What we collect as a controller
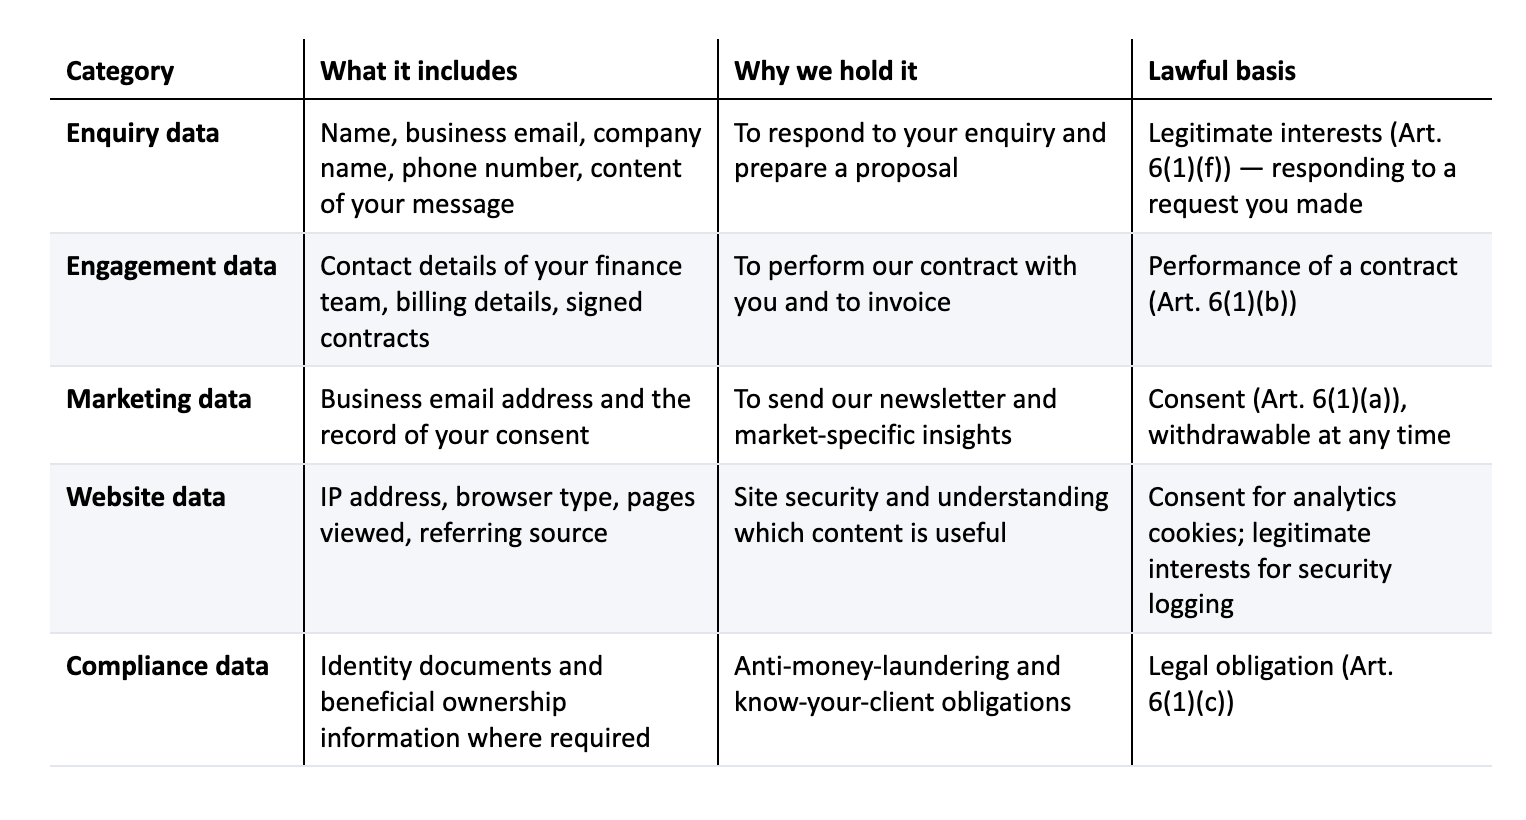
4.1 We do not collect special category data about website visitors or prospective clients. Where special category data reaches us in delivering payroll services — for example sickness absence records — we handle it strictly as a processor under section 9, never as a controller.
4.2 We do not carry out automated decision-making or profiling producing legal effects concerning you.
5. Cookies
5.1 Our website uses strictly necessary cookies, which cannot be disabled because the site will not function without them, and optional analytics cookies, which run only if you consent through our cookie banner.
5.2 You can withdraw cookie consent at any time using the cookie settings link in our footer, or by clearing cookies in your browser.
5.3 We do not use advertising or cross-site tracking cookies.
6. Who we share data with
6.1 We share personal data only with the categories of recipient below, and only so far as necessary:
(a) Cloud accounting and productivity providers hosting the systems we work in, listed in Annex III to our Data Processing Agreement.
(b) Professional advisers — our lawyers, auditors, and insurers — where they need the information to advise us.
(c) Regulators, tax authorities, and law enforcement where we are legally obliged to disclose.
6.2 We never sell personal data, and never share it for another organisation's marketing purposes.
7. International transfers
7.1 Our delivery team is located in Bangladesh. Personal data we process — whether as controller or processor — is accessed and processed by our staff in Dhaka. Data is also accessible from the United Arab Emirates and the United Kingdom.
7.2 Bangladesh is not the subject of an adequacy decision under Article 45 of the EU GDPR, nor of UK adequacy regulations. Transfers to Karifin therefore rely on the following safeguards:
(a) From the EEA: the Standard Contractual Clauses adopted by the European Commission in Implementing Decision (EU) 2021/914.
(b) From the United Kingdom: the International Data Transfer Addendum issued by the Information Commissioner under section 119A of the Data Protection Act 2018, appended to those Standard Contractual Clauses.
7.3 Before relying on these safeguards we carry out and document a transfer assessment covering the legal environment in Bangladesh, including any laws permitting public authority access to data. We follow the European Data Protection Board methodology for EEA transfers and the Information Commissioner's transfer risk assessment methodology for UK transfers. Both are reviewed at least annually.
7.4 Client data is hosted in EU or UK data centres operated by the providers listed in Annex III. Our Bangladesh personnel access that data remotely under controlled conditions; we do not export bulk client data to Bangladesh.
7.5 We apply supplementary technical measures to every transfer — encryption in transit and at rest, strict role-based access control, and a prohibition on storing client data on local devices. These are described in Annex II.
7.6 You may request a copy of the transfer safeguards we rely on by writing to [privacy@karifinco.com].
8. Your rights
8.1 Under both the EU GDPR and the UK GDPR you have the right to:
(a) be told what personal data we hold about you and receive a copy of it (Article 15);
(b) have inaccurate data corrected (Article 16);
(c) have your data erased where we no longer have grounds to keep it (Article 17);
(d) restrict how we use your data while a dispute about it is resolved (Article 18);
(e) receive your data in a portable, machine-readable format (Article 20);
(f) object to processing carried out on the basis of legitimate interests (Article 21); and
(g) withdraw consent at any time, without affecting processing carried out before withdrawal (Article 7(3)).
8.2 To exercise any of these rights, write to [privacy@karifinco.com]. We respond within one month. If your request is complex we may extend by two further months, and we will tell you within the first month if we do.
8.3 If your personal data reached us because you are an employee, supplier, or customer of one of our clients, we act as a processor and cannot decide your request. Please contact that organisation, which is the controller. If you contact us, we forward your request to them without undue delay and confirm to you that we have done so.
Complaints
8.4 If you are unhappy with how we have handled your personal data or your request, tell us first at [nasif@karifinco.com], marking your message "Data protection complaint". We acknowledge complaints within five working days, investigate, and give you a reasoned written response within one month.
8.5 If you remain dissatisfied, you may complain to a supervisory authority:
(a) Lithuania: State Data Protection Inspectorate (Valstybinė duomenų apsaugos inspekcija), L. Sapiegos g. 17, LT-10312 Vilnius, ada@ada.lt, +370 5 271 2804.
(b) Elsewhere in the EEA: the supervisory authority in the member state where you live, work, or where the alleged infringement took place.
(c) United Kingdom: Information Commissioner's Office, Wycliffe House, Water Lane, Wilmslow, Cheshire SK9 5AF, ico.org.uk, 0303 123 1113.
8.6 Complaining to us first does not affect your right to go to a supervisory authority at any time.
9. How we handle client data as a processor
9.1 Every client engagement is governed by a written Data Processing Agreement meeting the requirements of Article 28(3) of the EU GDPR and the UK GDPR. It is executed before we receive any personal data, and provided at no cost.
9.2 Under that agreement we commit to:
(a) process personal data only on the client's documented instructions;
(b) bind every member of staff with access to a written confidentiality obligation surviving the end of their engagement;
(c) maintain the technical and organisational security measures in Annex II;
(d) engage no new sub-processor without prior notice and an opportunity to object;
(e) notify the client without undue delay, and in any event within 24 hours, of becoming aware of a personal data breach;
(f) assist the client with data subject requests and data protection impact assessments; and
(g) delete or return all personal data at the end of the engagement, at the client's choice.
9.3 A copy of our standard Data Processing Agreement is available at [karifinco.com/dpa] or on request at [privacy@karifinco.com].
10. How long we keep data
10.1 Enquiry data that does not lead to an engagement: 12 months from last contact.
10.2 Client engagement records, including contracts and correspondence: seven years from the end of the engagement, to meet accounting and professional record-keeping obligations.
10.3 Marketing data: until you withdraw consent, or after 24 months without engagement with our emails, whichever comes first.
10.4 Personal data processed on behalf of a client: for the period set out in that client's Data Processing Agreement, and no longer.
11. Changes to this statement
11.1 We review this statement at least annually. Where we make a material change we update the date at the top and notify existing clients' engagement contacts by email.
PART B · FOR EXECUTION WITH EACH CLIENT
Data Processing Agreement
This Data Processing Agreement (the "DPA") forms part of and is subject to the engagement letter or services agreement between the parties (the "Principal Agreement"). Where this DPA conflicts with the Principal Agreement on a matter of data protection, this DPA prevails.
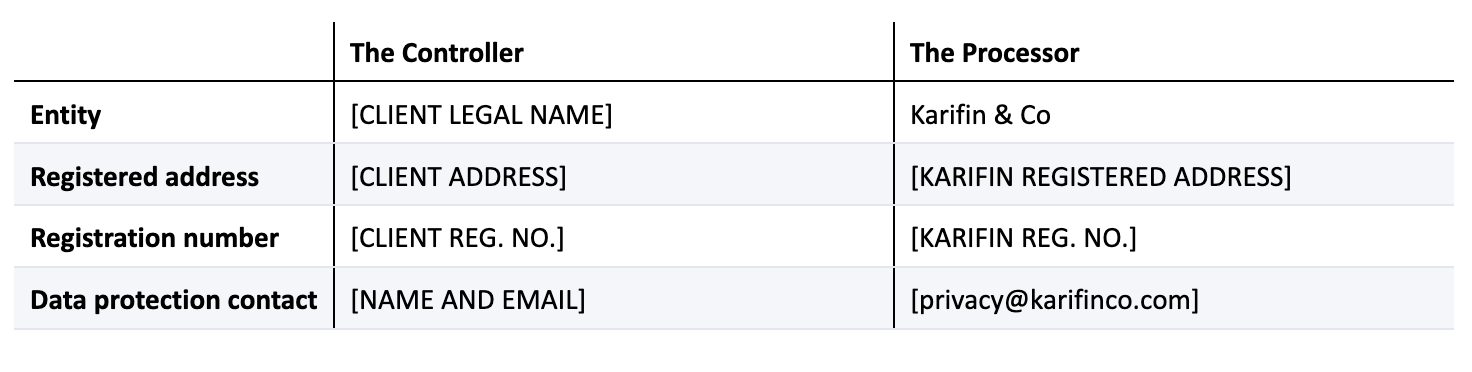
Parties
Jurisdiction schedule
Complete this schedule before signature. The elections made here determine which of the tagged clauses below take effect, and govern the whole of this DPA.
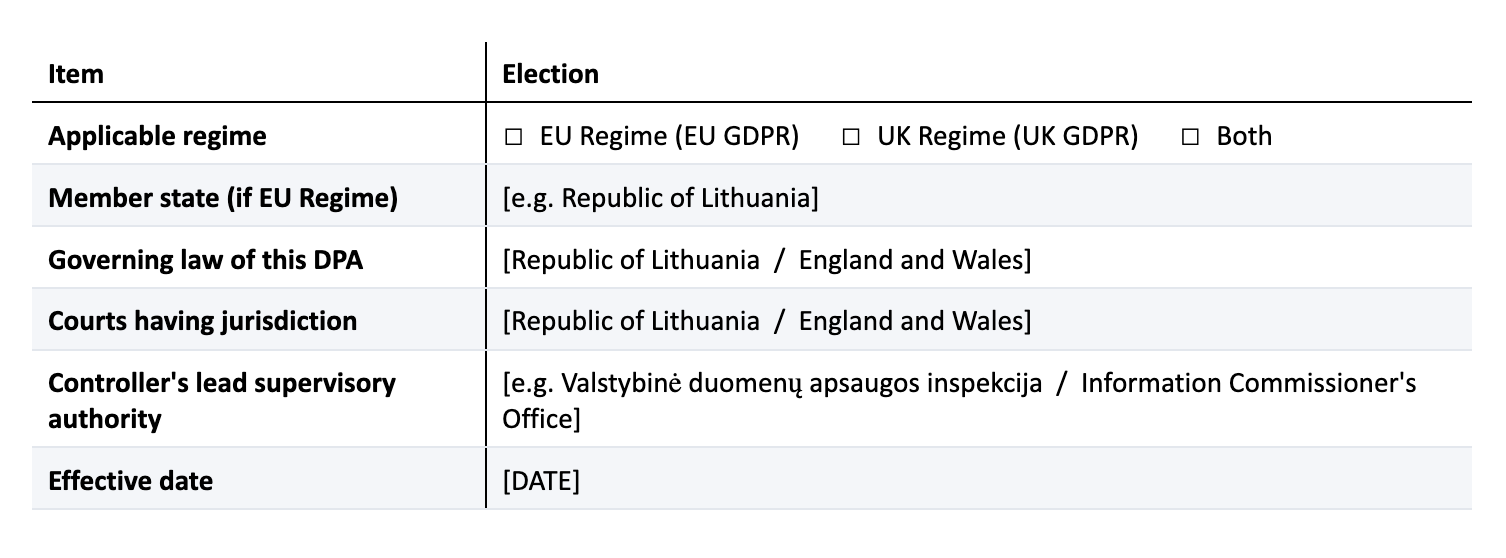
Where "Both" is elected, every clause tagged EU REGIME and every clause tagged UK REGIME applies, and the parties execute both the EU Standard Contractual Clauses and the UK Addendum.
1. Definitions
1.1 "EU GDPR" means Regulation (EU) 2016/679, together with the national implementing legislation of the member state identified in the jurisdiction schedule.
1.2 "UK GDPR" has the meaning given in section 3(10) of the Data Protection Act 2018, read with the Data (Use and Access) Act 2025.
1.3 "Applicable Data Protection Law" means the EU GDPR where the EU Regime is elected, the UK GDPR where the UK Regime is elected, and both where "Both" is elected. Where both apply, the higher standard governs in respect of each obligation.
1.4 The terms "personal data", "processing", "controller", "processor", "data subject", "personal data breach", and "supervisory authority" carry the meanings given in Article 4 of the Applicable Data Protection Law.
1.5 "Sub-processor" means any third party engaged by Karifin to process personal data on the Controller's behalf.
1.6 "EU SCCs" means the standard contractual clauses for transfers to third countries adopted by the European Commission in Implementing Decision (EU) 2021/914 of 4 June 2021.
1.7 "UK Addendum" means the International Data Transfer Addendum to the EU Commission Standard Contractual Clauses, version B1.0, issued by the Information Commissioner under section 119A of the Data Protection Act 2018.
2. Roles and scope
2.1 The Controller is the controller of the personal data described in Annex I. Karifin is the processor.
2.2 Karifin processes personal data only for the purposes in Annex I and only for as long as necessary for those purposes.
2.3 The Controller warrants that it has a lawful basis for the processing it instructs, that it has issued any required privacy notice to the relevant data subjects, and that its instructions do not require Karifin to breach the Applicable Data Protection Law.
2.4 Nothing in this DPA makes Karifin a controller. If Karifin determines the purposes and means of any processing, it becomes a controller for that processing and is separately responsible for it.
3. Processing on documented instructions
3.1 Karifin processes personal data only on the Controller's documented instructions, including as to international transfers, unless required to process by law to which Karifin is subject. Where such a requirement applies, Karifin informs the Controller before processing unless that law prohibits it on important grounds of public interest.
3.2 The Principal Agreement, this DPA, and Annex I together constitute the Controller's complete initial instructions. Further instructions must be given in writing to [privacy@karifinco.com].
3.3 Karifin informs the Controller immediately if, in its opinion, an instruction infringes the Applicable Data Protection Law, and may suspend that instruction until it is confirmed, amended, or withdrawn.
4. Confidentiality
4.1 Karifin ensures that every person authorised to process the personal data — employee, contractor, or officer — has committed to confidentiality in writing, or is under an appropriate statutory obligation of confidentiality.
4.2 Those obligations survive the termination of that person's engagement with Karifin.
4.3 Karifin limits access to personnel who need it to deliver the services, and applies role-based access control to enforce this.
5. Security
5.1 Karifin implements and maintains the technical and organisational measures in Annex II, designed to ensure a level of security appropriate to the risk, taking account of the state of the art, cost of implementation, and the nature, scope, context, and purposes of the processing.
5.2 Karifin may update Annex II provided the overall level of security is not reduced. Material reductions require the Controller's prior written agreement.
5.3 Karifin regularly tests, assesses, and evaluates the effectiveness of these measures, and keeps a record of having done so.
6. Sub-processors
6.1 The Controller gives Karifin general written authorisation to engage sub-processors, subject to this clause 6.
6.2 The sub-processors engaged at the effective date are listed in Annex III and are deemed approved.
6.3 Karifin gives at least 30 days' written notice before adding or replacing a sub-processor. The Controller may object on reasonable data protection grounds within 14 days.
6.4 If the parties cannot resolve an objection within 30 days, either may terminate the affected services on written notice, without penalty to the Controller.
6.5 Karifin imposes on each sub-processor, by written contract, data protection obligations no less protective than those in this DPA, and remains fully liable to the Controller for any sub-processor failure.
7. International transfers
7.1 The Controller acknowledges that Karifin processes personal data in Bangladesh, and that data may be accessed from the United Arab Emirates and the United Kingdom.
7.2 Bangladesh is not the subject of an adequacy decision under Article 45 of the EU GDPR, nor of adequacy regulations under section 17A of the Data Protection Act 2018.
EU REGIME
7.3 Where the EU Regime is elected, the parties enter into the EU SCCs, incorporated by reference and taking effect as follows:
(a) Module Two (controller to processor) applies. The Controller is the data exporter; Karifin is the data importer.
(b) Clause 7 (docking clause) is included.
(c) In Clause 9, Option 2 (general written authorisation) applies, with a notice period of 30 days as set out in clause 6.3 above.
(d) In Clause 11, the optional independent redress provision is not included.
(e) In Clause 17, the EU SCCs are governed by the law of the member state identified in the jurisdiction schedule.
(f) In Clause 18(b), disputes are resolved before the courts of that member state.
(g) Annexes I, II, and III to this DPA populate the corresponding annexes to the EU SCCs.
UK REGIME
7.4 Where the UK Regime is elected, the parties enter into the EU SCCs as modified by the UK Addendum, taking effect as follows:
(a) Table 1 of the UK Addendum is completed with the parties' details as set out above.
(b) Table 2 identifies the EU SCCs, Module Two, as the Approved EU SCCs to which the Addendum is appended, with the selections at clause 7.3(b) to (d) above.
(c) Table 3 is populated by Annexes I, II, and III to this DPA.
(d) In Table 4, neither party may end the Addendum as set out in Section 19 of the Addendum.
(e) The UK Addendum is governed by the law of England and Wales, and the courts of England and Wales have jurisdiction.
7.5 As an alternative to clause 7.4, the parties may agree in writing to use the Information Commissioner's standalone International Data Transfer Agreement. Where they do, that agreement replaces clause 7.4 and the EU SCCs do not apply to UK transfers.
7.6 Karifin warrants that it has no reason to believe the laws of Bangladesh applicable to it prevent it from fulfilling its obligations under the transfer mechanism elected, and that it has carried out and documented an assessment of that legal environment. That assessment follows the European Data Protection Board methodology for EEA transfers and the Information Commissioner's transfer risk assessment methodology for UK transfers.
7.7 Karifin notifies the Controller promptly if it becomes unable to comply with the elected mechanism. The Controller may then suspend transfers or terminate the affected services.
7.8 Karifin applies the supplementary measures in Annex II, Part 3, to every transfer.
7.9 The Controller acknowledges that data is hosted in EU or UK data centres as set out in Annex III. Transfers of personal data between the EEA and the United Kingdom rely on the mutual adequacy findings in force between those jurisdictions and require no separate safeguard for so long as those findings subsist.
8. Assistance with data subject rights
8.1 Karifin implements appropriate technical and organisational measures to assist the Controller in responding to data subject requests under Chapter III of the Applicable Data Protection Law.
8.2 If a data subject contacts Karifin directly, Karifin does not respond to the substance. It forwards the request to the Controller without undue delay, and in any event within three working days.
8.3 Karifin provides the assistance the Controller reasonably requires to respond within the statutory deadline. Where that assistance goes materially beyond the ordinary scope of the services, Karifin may charge at its standard rates, having first notified the Controller of the expected cost.
9. Personal data breaches
9.1 Karifin notifies the Controller without undue delay, and in any event within 24 hours, of becoming aware of a personal data breach affecting the Controller's personal data.
9.2 The notification includes, so far as known at the time:
(a) the nature of the breach, including the categories and approximate number of data subjects and records concerned;
(b) the name and contact details of Karifin's data protection contact point;
(c) the likely consequences of the breach; and
(d) the measures taken or proposed to address it and mitigate its effects.
9.3 Where full information is not available within 24 hours, Karifin provides what it has and supplies the remainder in phases without further undue delay.
9.4 Karifin does not notify any supervisory authority or data subject unless legally required, or unless the Controller instructs it in writing. The decision to notify rests with the Controller.
9.5 Karifin maintains a record of all personal data breaches affecting the Controller's data, including facts, effects, and remedial action, available to the Controller on request.
10. Data protection impact assessments
10.1 Karifin provides reasonable assistance with data protection impact assessments under Article 35 of the Applicable Data Protection Law, and with any prior consultation with a supervisory authority under Article 36, taking into account the nature of the processing and the information available to Karifin.
11. Audit and information rights
11.1 Karifin makes available all information necessary to demonstrate compliance with Article 28 of the Applicable Data Protection Law and with this DPA.
11.2 Karifin allows for and contributes to audits, including inspections, by the Controller or an auditor it mandates, subject to clauses 11.3 and 11.4.
11.3 Audits take place on at least 30 days' written notice, during normal business hours, no more than once in any 12-month period, and must not unreasonably disrupt operations. The frequency limit does not apply following a personal data breach, or where a supervisory authority requires an audit.
11.4 Any auditor must sign a confidentiality undertaking before access. Each party bears its own costs, unless the audit reveals a material breach by Karifin, in which case Karifin reimburses the Controller's reasonable costs.
11.5 Karifin may satisfy an audit request by providing a current third-party certification or audit report where that report reasonably addresses the Controller's enquiry.
12. Return and deletion
12.1 On termination of the services, and at the Controller's written election, Karifin either returns all personal data or deletes it.
12.2 The Controller must elect within 30 days of termination. Failing an election, Karifin deletes the personal data.
12.3 Return is made in a structured, commonly used, machine-readable format within 30 days of the election.
12.4 Karifin may retain personal data so far as required by law, or by the professional record-keeping obligations to which it is subject as an accountancy practice. Data so retained is kept only as long as the obligation requires, remains subject to this DPA, and is not processed for any other purpose.
12.5 Karifin certifies deletion in writing on request.
13. Liability
13.1 Each party is liable for damage caused by processing that infringes the Applicable Data Protection Law, in accordance with Article 82.
13.2 Liability under this DPA is subject to the limitations and exclusions in the Principal Agreement, except that nothing limits either party's liability for a fine imposed on it directly by a supervisory authority, or for death, personal injury, or fraud.
13.3 This clause does not limit the rights of data subjects under the EU SCCs or the UK Addendum.
14. Term, governing law, and signature
14.1 This DPA takes effect on the effective date in the jurisdiction schedule and continues for as long as Karifin processes personal data on the Controller's behalf. Clauses 4, 12, and 13 survive termination.
14.2 This DPA is governed by the law identified in the jurisdiction schedule, and the courts identified there have exclusive jurisdiction — without prejudice to clauses 7.3(e), 7.3(f), and 7.4(e), which govern the transfer mechanisms themselves.
14.3 Amendments must be in writing and signed by both parties. Where a change in law requires amendment, the parties negotiate in good faith to agree it promptly. This includes any replacement of the EU SCCs or the UK Addendum by a successor instrument, which the parties will adopt within the transition period allowed.
PART C · ANNEXES TO THE DPA
Processing details, security measures, sub-processors

